CVE-2024-26152Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
- 4.7MediumCVSS base score
- 2.2%Exploitation in 30 daysEPSS · top 17% of all CVEs
- NoKnown exploitednot in CISA's KEV catalog
- YesPublic exploitsa reference or SSVC says so
Description
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 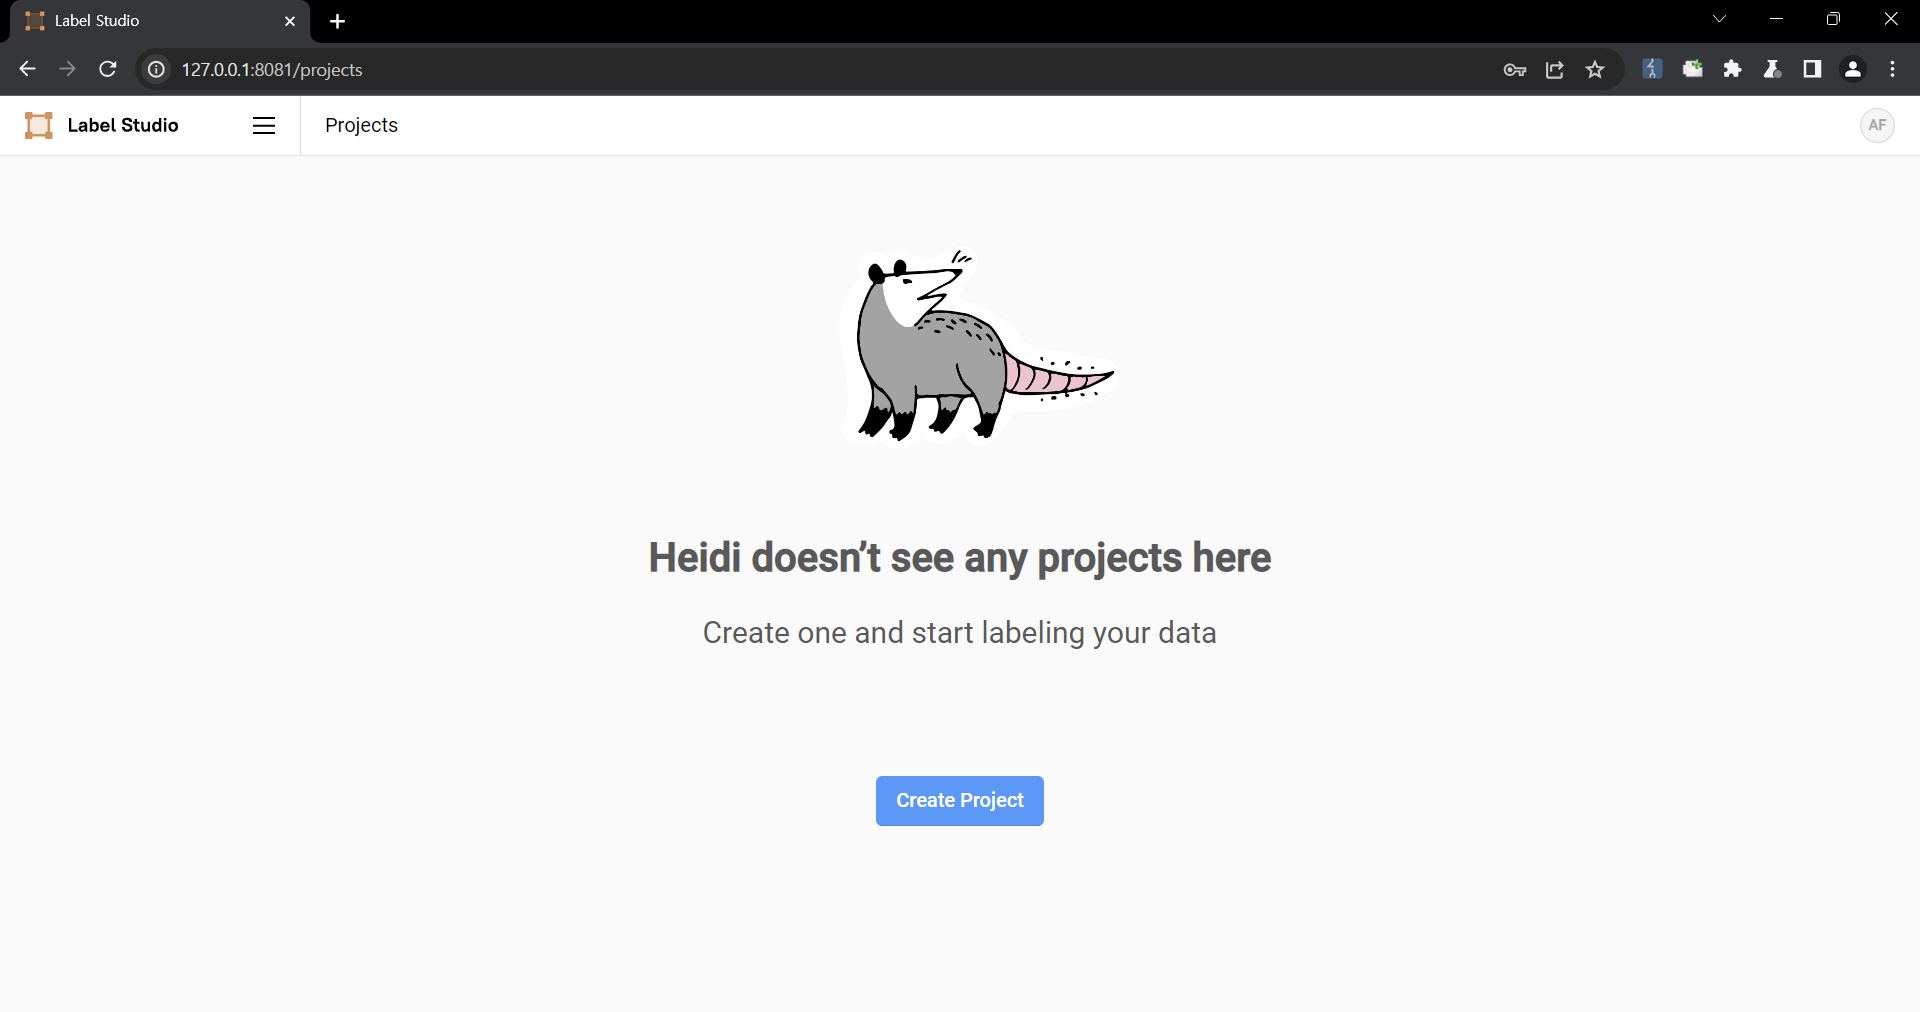 2. Upload a file containing the payload using the "Upload Files" function. 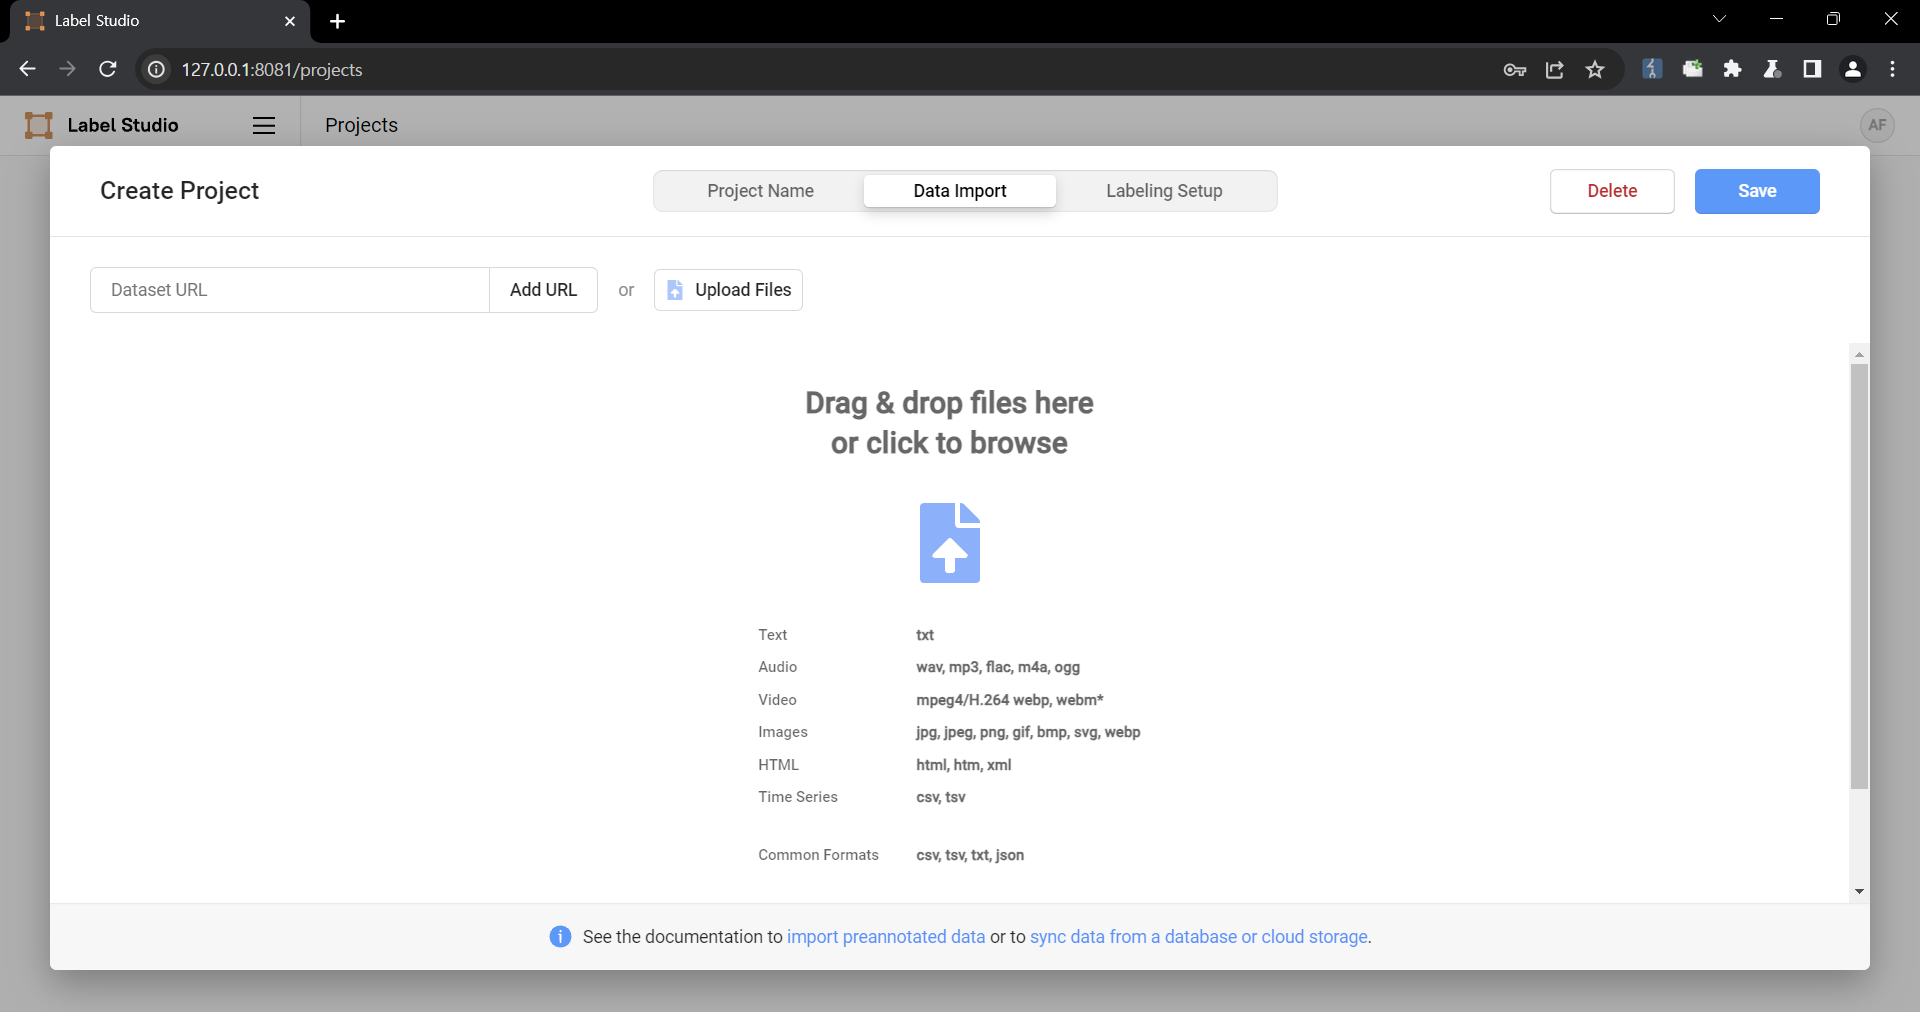 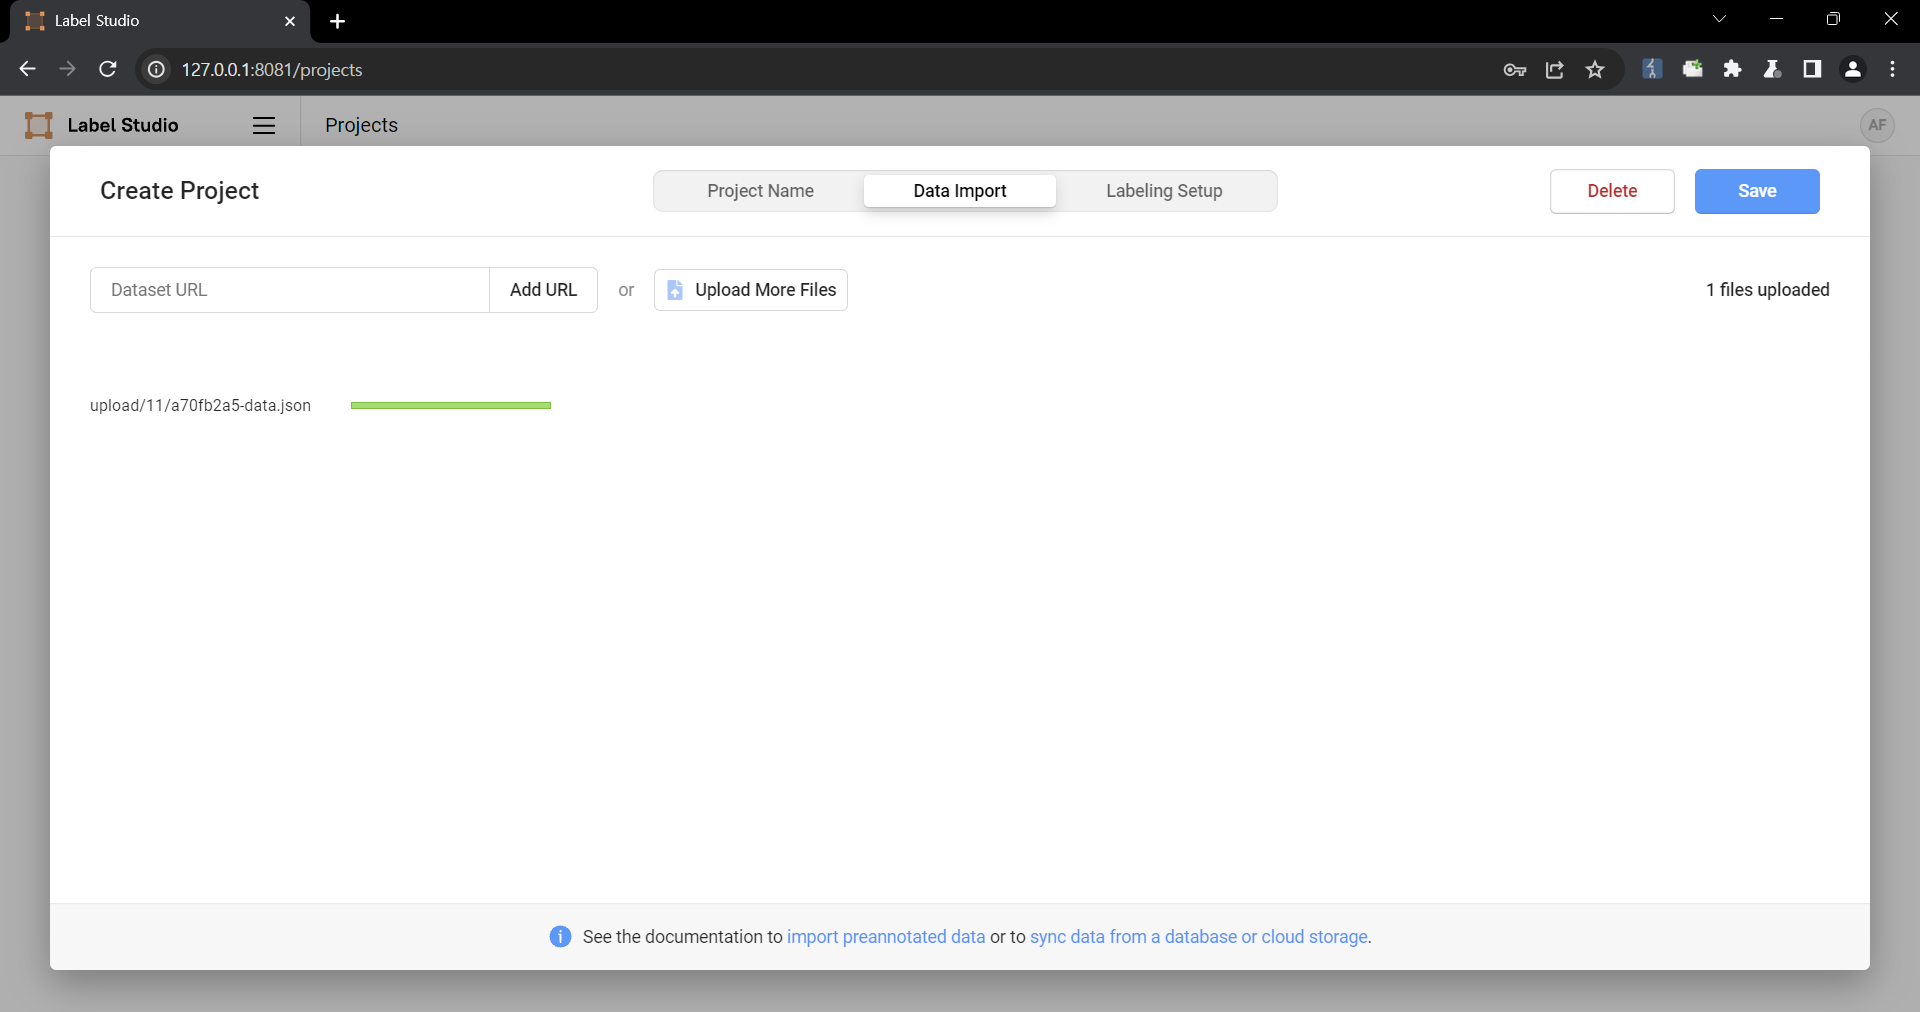 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 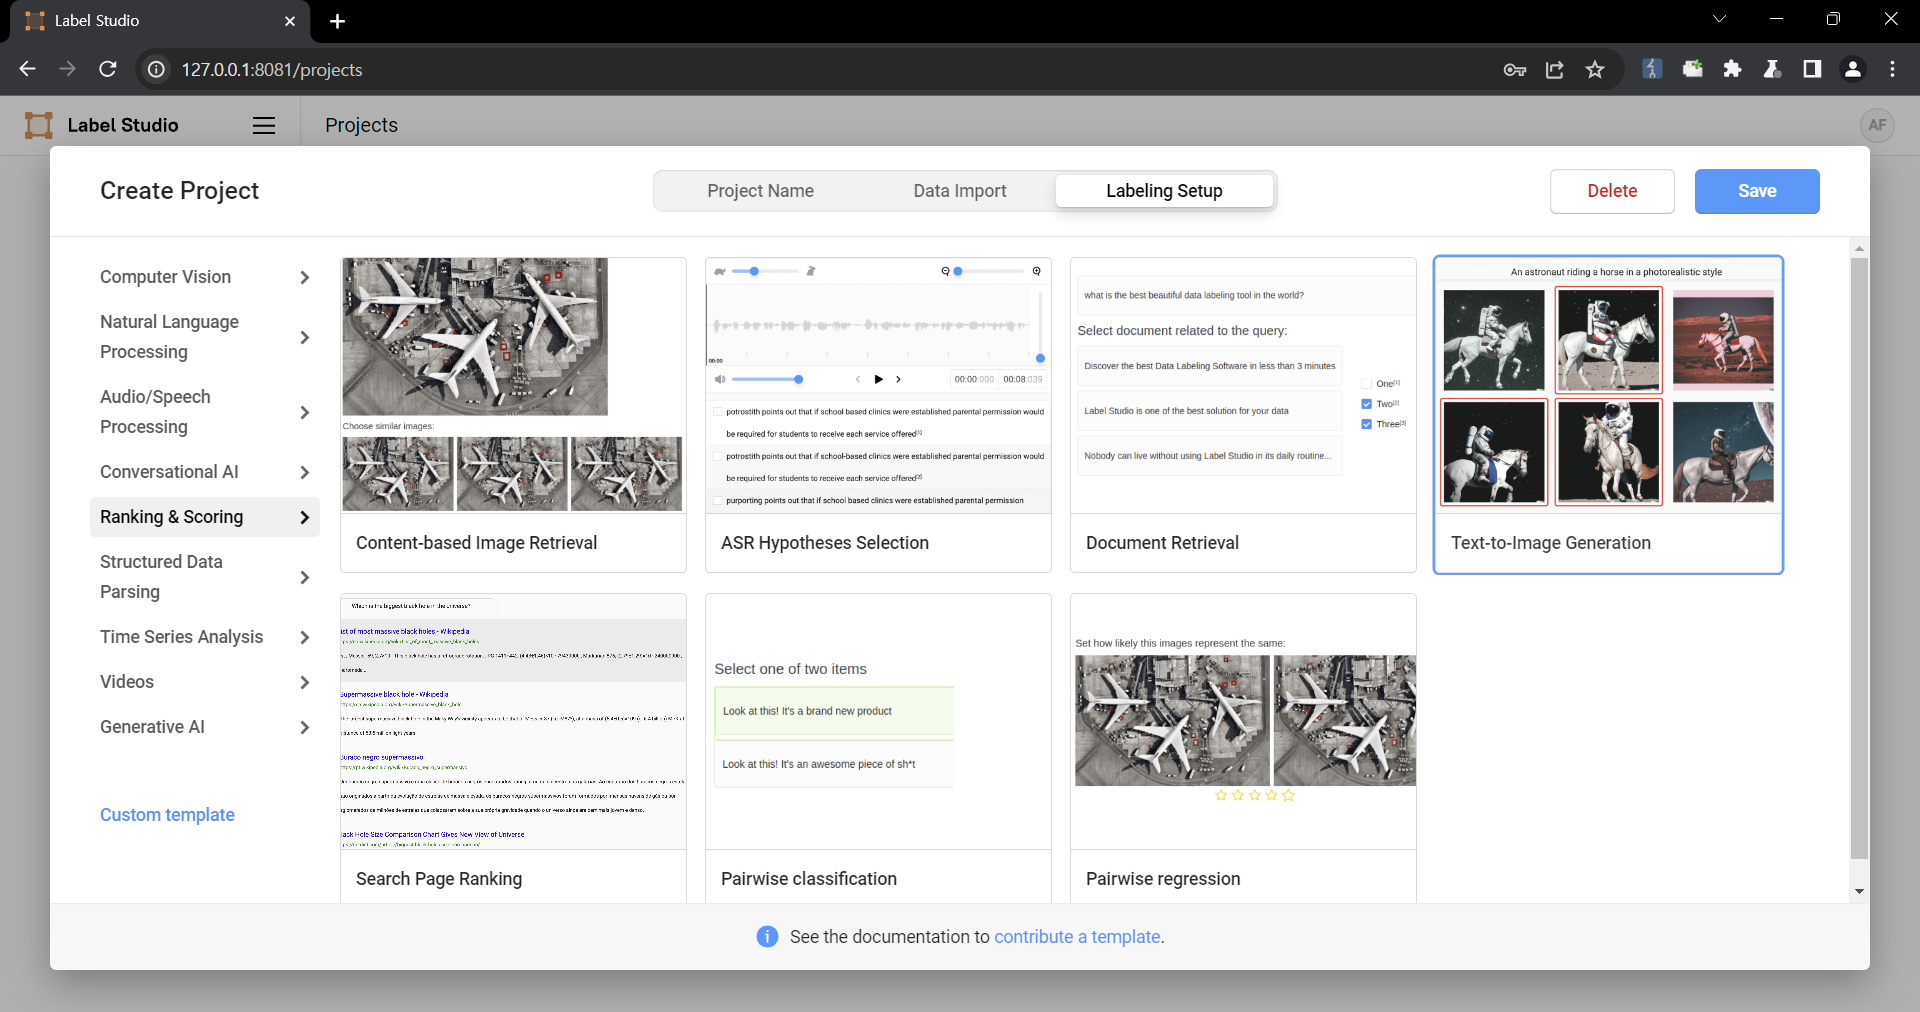 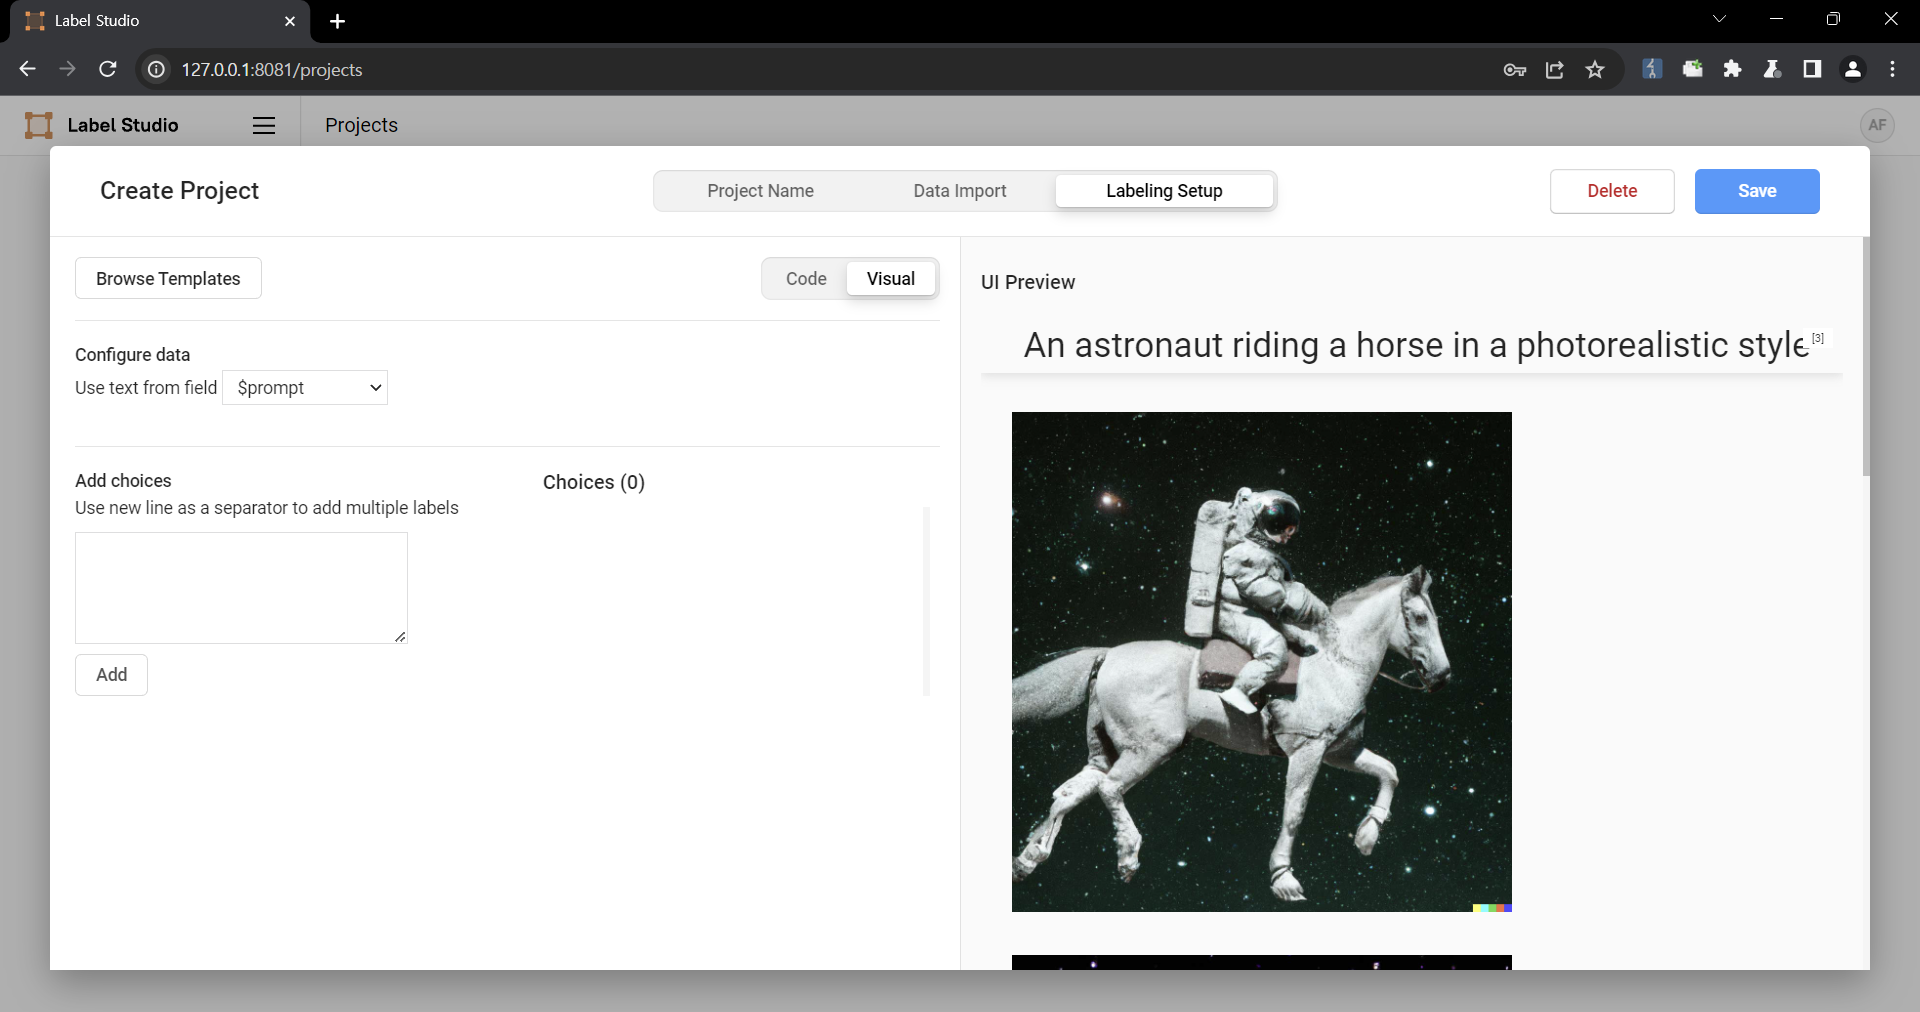 4. Select a task 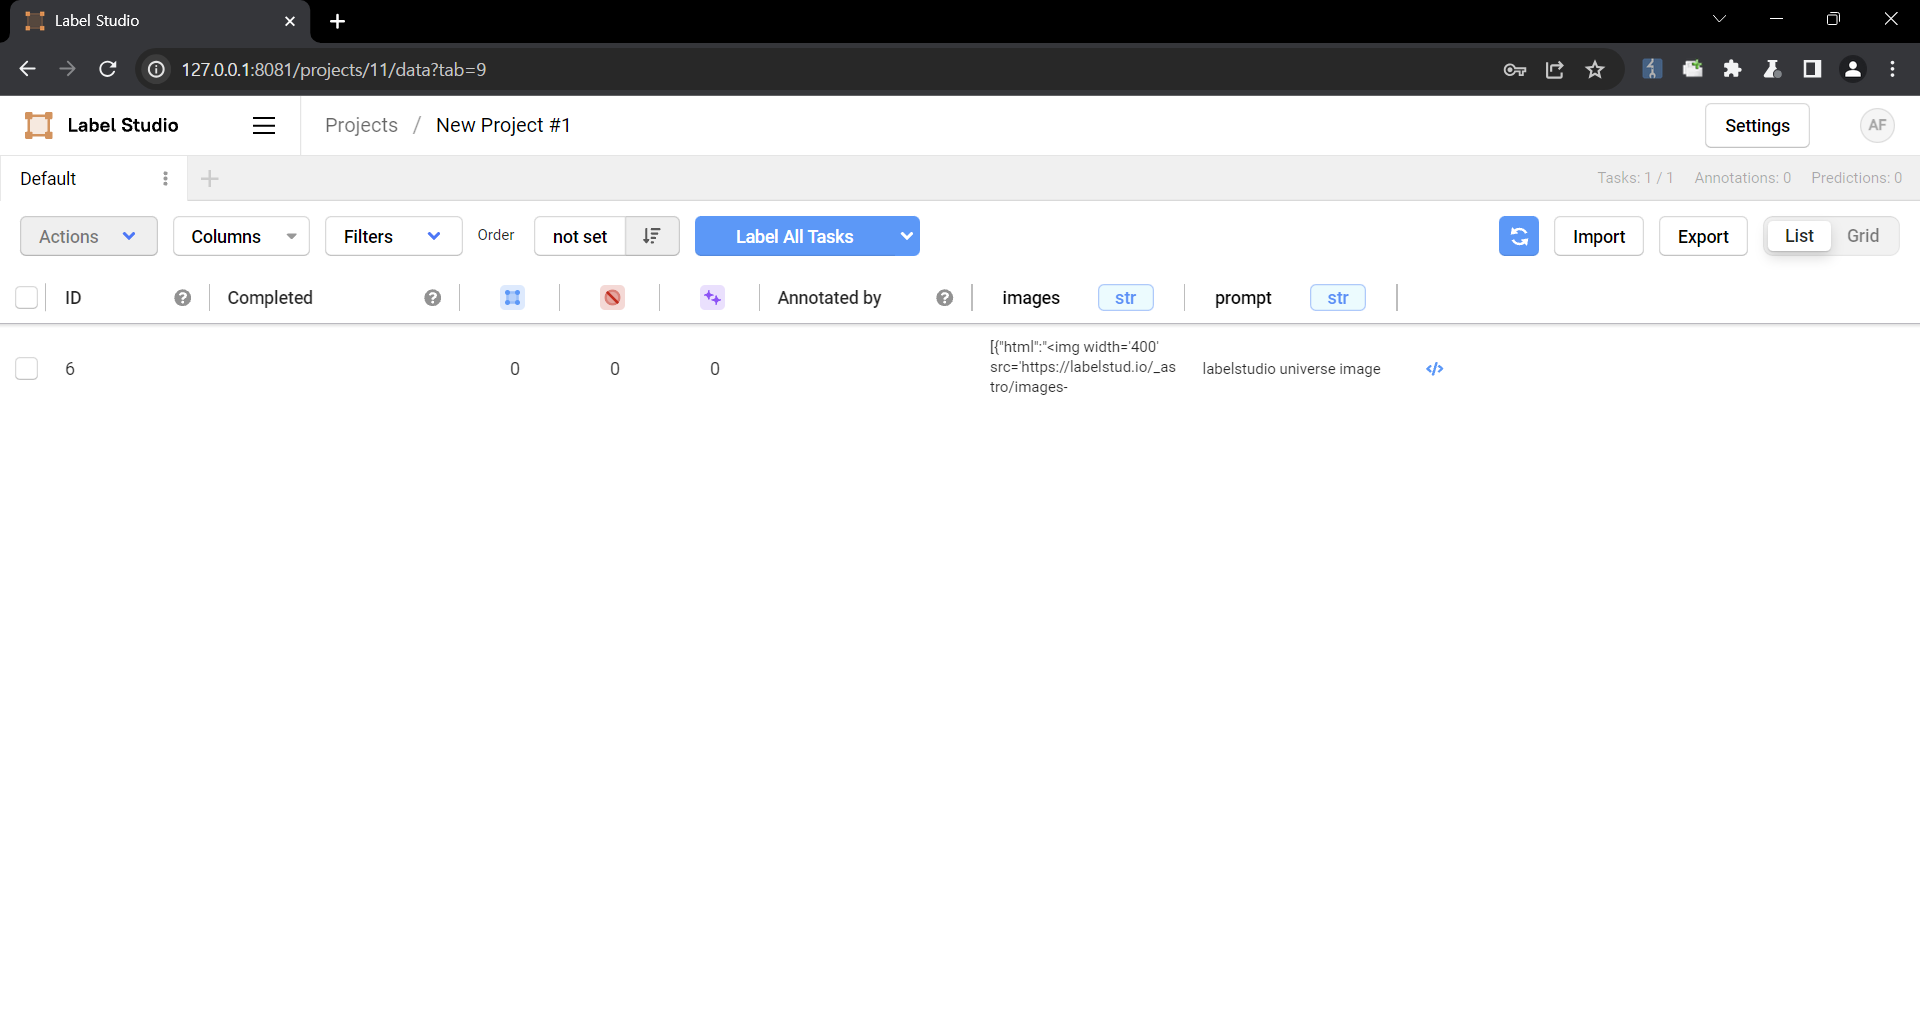 5. Check that the script is running 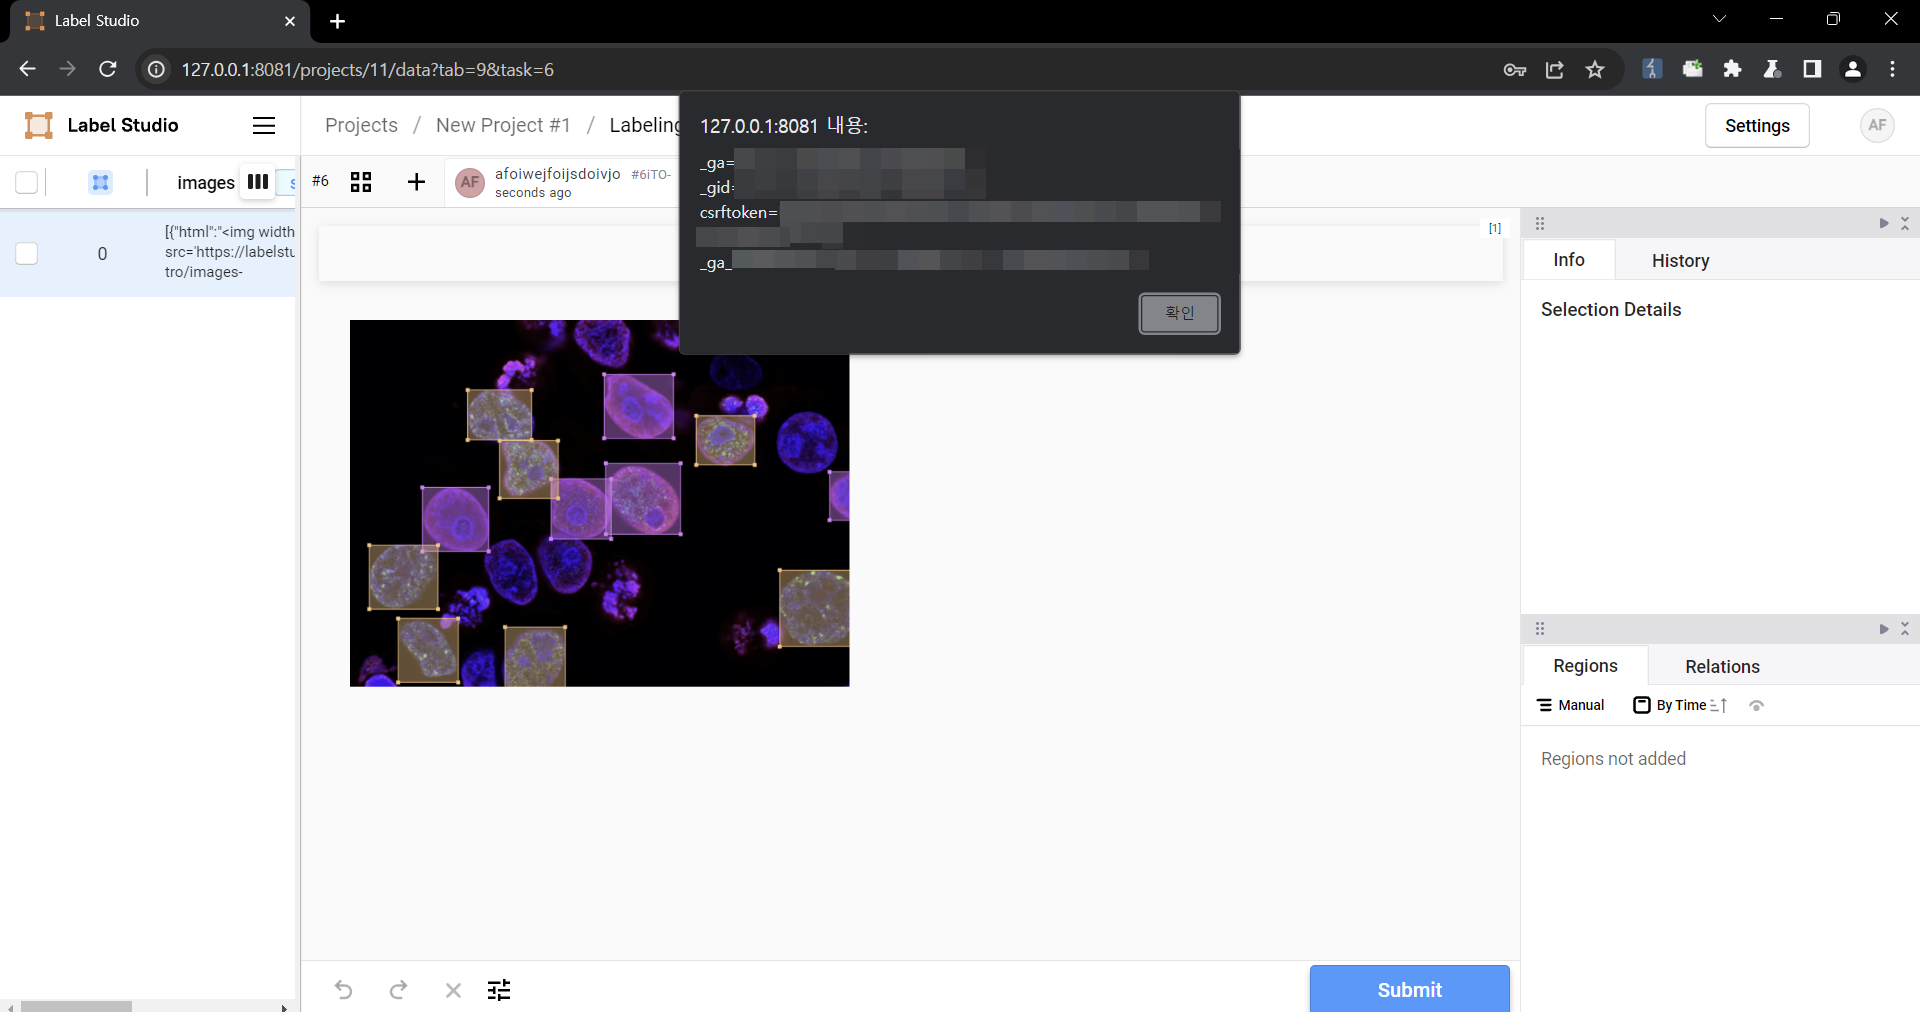 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Public exploit
An exploit or proof of concept is public: anyone can try it against an unpatched system. CISA's SSVC rates its exploitation: a proof of concept is public.
Timeline
ID reserved
By GitHub_M
- 8 days later
· 8 days later
Published
- 6 months later
· 6 months later
Record updated
Changes after publication (a new score, a public exploit, EPSS crossing 1, 10 or 50 %, leaving KEV) are kept since November 2026; earlier ones are not known.
Scores
| Scored by | CVSS | Score | Vector |
|---|---|---|---|
| GitHub_MCNA (assigner) | 3.1 | Medium4.7 | CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N |
| NVDNVD · Analyzed | 3.1 | Medium6.1 | CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N |
- EPSS (exploitation in 30 days)
- 2.2% · top 17% of all CVEs (16 Nov 2026)
- CISA SSVC
- Exploitation: poc · Automatable: no · Technical impact: partial
The list uses the assigner's score when there is one, then CISA's, then NVD's: Medium 4.7.
Affected products
- affected < 1.11.0
Affected packages
From reviewed advisories of the GitHub Advisory Database.
- PyPIlabel-studioGHSA-6xv9-957j-qfhg (opens in a new tab)
References
References4
- https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg (opens in a new tab)x_refsource_CONFIRMx_transferred
- https://github.com/HumanSignal/label-studio/pull/5232 (opens in a new tab)x_refsource_MISCx_transferred
- https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8 (opens in a new tab)x_refsource_MISCx_transferred
- https://github.com/HumanSignal/label-studio/releases/tag/1.11.0 (opens in a new tab)x_refsource_MISCx_transferred
Sources
The same CVE in the primary databases and aggregators, to check against.
- CVE.org record (opens in a new tab)
- CVE List JSON (GitHub) (opens in a new tab)
- NVD (opens in a new tab)
- FIRST EPSS (opens in a new tab)
- EUVD EUVD-2024-0544 (opens in a new tab)
- OSV.dev (opens in a new tab)
- GitHub Advisory GHSA-6xv9-957j-qfhg (opens in a new tab)
- CIRCL Vulnerability-Lookup (opens in a new tab)
Badge for a README or a ticket

[](https://cveledger.app/cve/CVE-2024-26152)Record last updated .